CCIE lab対策(2.4.b Inter-AS L3VPN)その1 Inter-AS option A
Inter-AS option A (IOS-XR)が理解できたので自分のメモ用にアウトプットします。
1. Inter-AS Option A とは
Inter-AS Option A とは、Inter-AS Link で VRF を使って back-to-back 接続する最もシンプルな方式です。
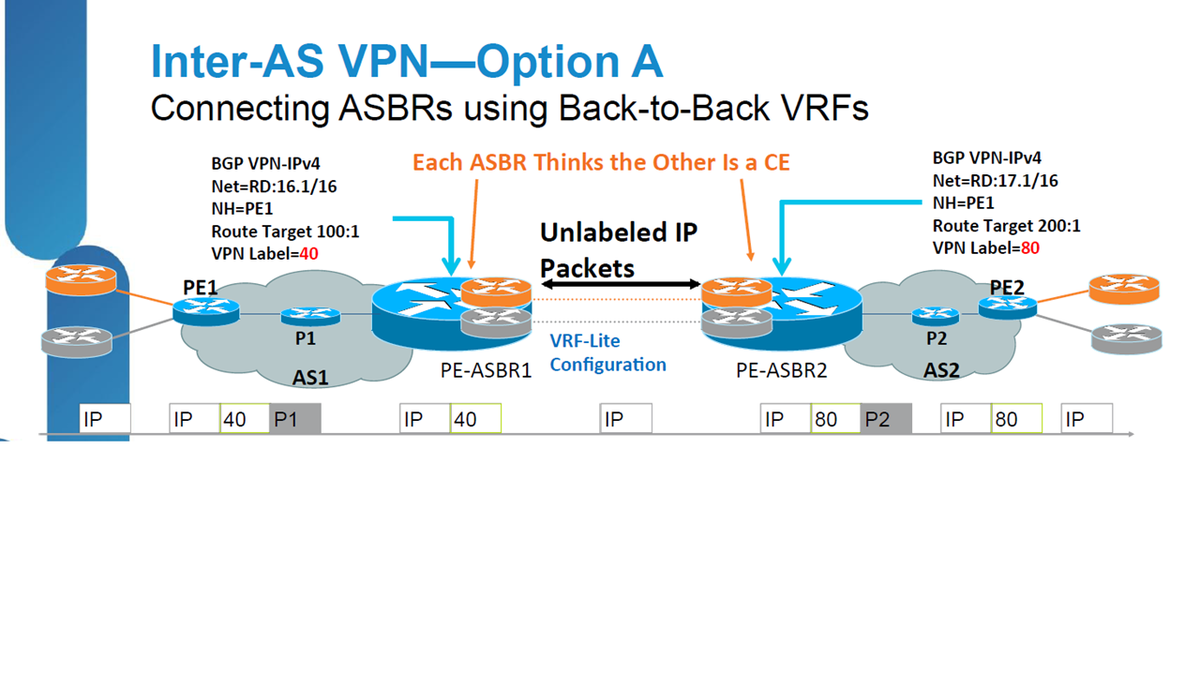
リンク先のドキュメントは素晴らしいので、Inter-AS 構成する方はきっと何かの助けになることでしょう。
https://nsrc.org/workshops/2015/apricot2015/raw-attachment/wiki/Track3MPLS/9-Apriot_2015_Inter-AS.2.pdf
ASBR-ASBR でVRF-Liteを構成するだけ!としか説明がない。確かにその通りなのですが...。
ポイントとしては、PE-ASBRはLDPを有効化します。これはCE-PEから受け取ったIP PayloadにVPNラベルを付与するためです。ASBR-ASBR間はVRF-Liteを構成します。route-targetで少しハマりました。仕組みが分かれば大した問題ではありません。
2. Topology
CE-PE-ASBR-ASBR-PE-CE を含めた最小構成としました。
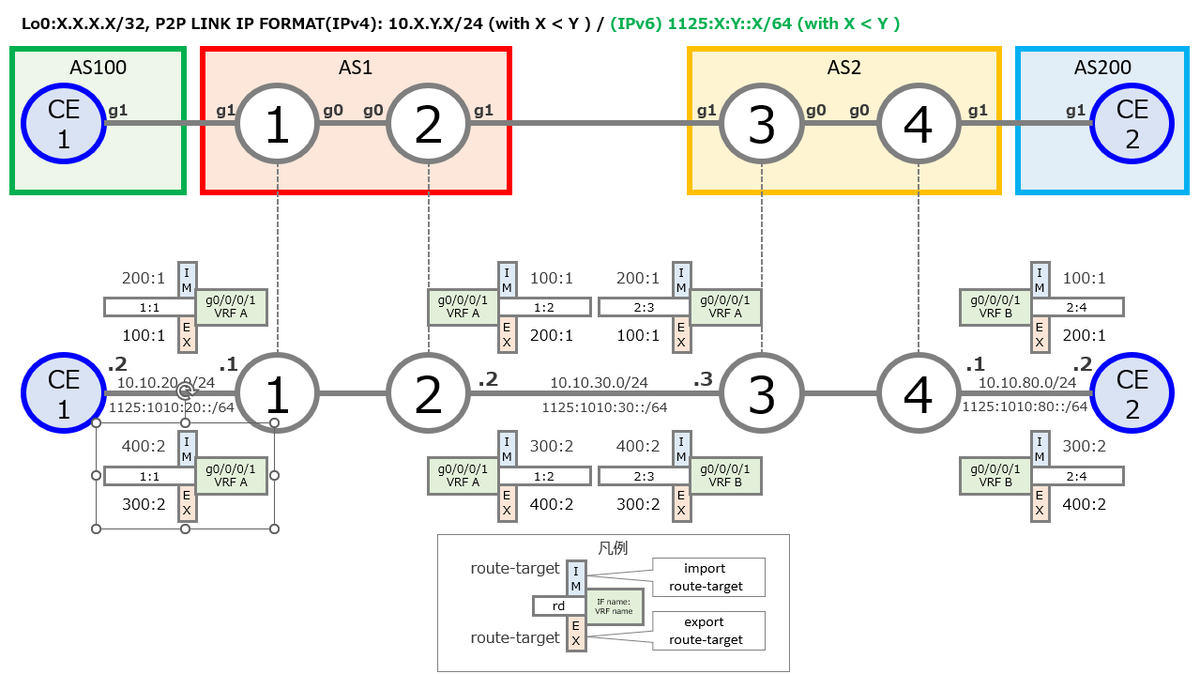
過去の検証では、route-target:RTやroute distinguisher:RDを揃えていることが多く正確には理解できていませんでした。 中途半端な理解でRDとRTを統一すると、正確に理解できなくなってしまうかもしれない。極端な例ですが。
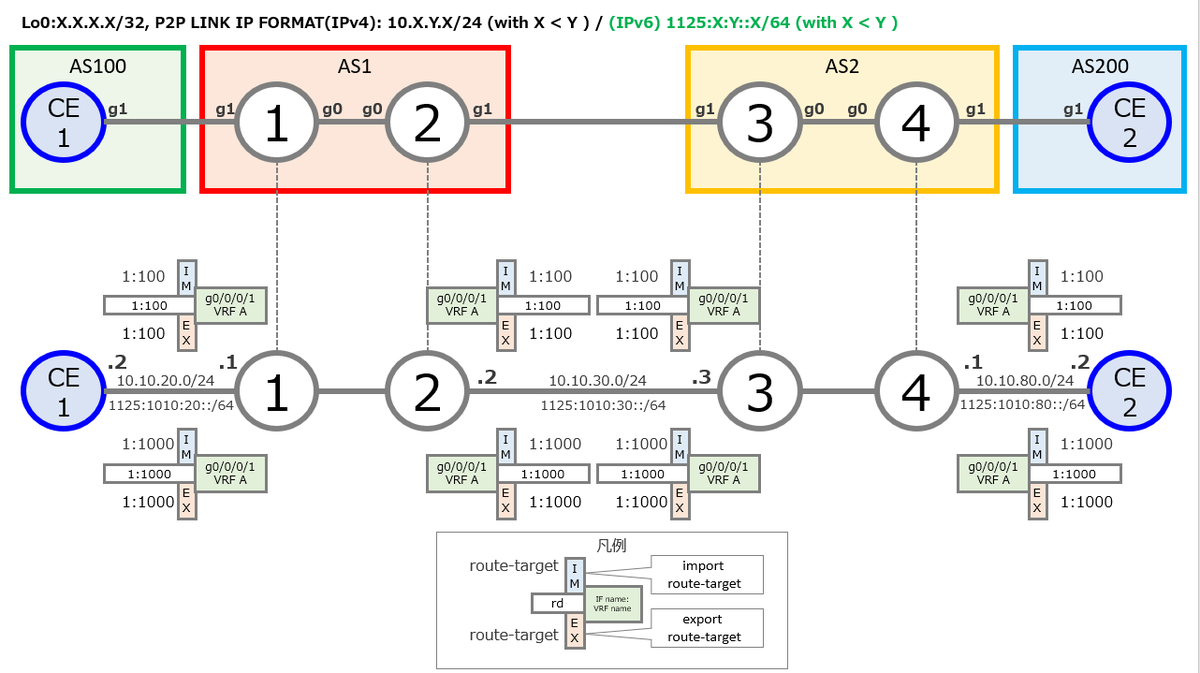
これでは、RTについて理解できなくなるのは当然です。そのため、今回は敢えてImport RTとExport RTを同一にしないようにしてみました。 しかし、いざ組んで見ると何をしたいのか分からないのです。最初はこうなると思っていました。

c_CE1#show ip route bgp | b Gate
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
B        10.10.80.0/24 [20/0] via 10.10.20.1, 22:12:45
      200.200.200.0/32 is subnetted, 1 subnets
B        200.200.200.200 [20/0] via 10.10.20.1, 22:12:45
c_CE1#
c_CE1#ping 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 200.200.200.200, timeout is 2 seconds:
Packet sent with a source address of 100.100.100.100
.....
Success rate is 0 percent (0/5)
c_CE1#
ルーティング情報は入ってくるけど、肝心のL3VPNが機能しません。
RP/0/RP0/CPU0:c_N2#show bgp vpnv4 unicast vrf A 200.200.200.200
Sun Jan 22 02:51:25.275 UTC
BGP routing table entry for 200.200.200.200/32, Route Distinguisher: 1:2
Versions:
  Process           bRIB/RIB  SendTblVer
  Speaker                 75          75
    Local Label: 24004
Last Modified: Jan 22 02:47:23.278 for 00:04:02
Paths: (1 available, best #1)
  Advertised to peers (in unique update groups):
    1.1.1.1
  Path #1: Received by speaker 0
  Advertised to peers (in unique update groups):
    1.1.1.1
  2 200
    10.10.30.3 from 10.10.30.3 (3.3.3.3)
      Origin IGP, localpref 100, valid, external, best, group-best, import-candidate
      Received Path ID 0, Local Path ID 1, version 75
      Extended community: RT:100:1 RT:200:1
RP/0/RP0/CPU0:c_N2#
もしかして、個々のVRFで完結するのではなくてクロスしてend-to-endで接続するでは? 何となくそう思い、ASBRのRTをテレコにしてみました。結論、正解でした!

これが何故正しいと言えるのかは後で説明します。
3. Config
c_N1のconfig
hostname c_N1
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf A
 rd 1:1
 address-family ipv4 unicast
  import route-target
   200:1
  !
  export route-target
   100:1
  !
 !
 address-family ipv6 unicast
  import route-target
   400:2
  !
  export route-target
   300:2
  !
 !
!
interface Loopback0
 ipv4 address 1.1.1.1 255.255.255.255
 ipv6 address 1125:1:1:1::1/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.1.2.1 255.255.255.0
 ipv6 address 1125:1:2::1/64
!
interface GigabitEthernet0/0/0/1
 vrf A
 ipv4 address 10.10.20.1 255.255.255.0
 ipv6 address 1125:1010:20::1/64
!
route-policy PASS
  pass
end-policy
!
router isis AS1
 apply-group CCIE-ISIS
 net 49.0001.0000.0000.0001.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 1
 bgp router-id 1.1.1.1
 address-family ipv4 unicast
 !
 address-family vpnv4 unicast
 !
 address-family ipv6 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 2.2.2.2
  remote-as 1
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:2:2:2::2
  remote-as 1
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf A
  rd 1:1
  address-family ipv4 unicast
   redistribute connected
  !
  address-family ipv6 unicast
   redistribute connected
  !
  neighbor 10.10.20.2
   remote-as 100
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:20::2
   remote-as 100
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
mpls oam
!
mpls ldp
 router-id 1.1.1.1
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
c_N2のconfig
hostname c_N2
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf A
 rd 1:2
 address-family ipv4 unicast
  import route-target
   100:1
  !
  export route-target
   200:1
  !
 !
 address-family ipv6 unicast
  import route-target
   300:2
  !
  export route-target
   400:2
  !
 !
!
interface Loopback0
 ipv4 address 2.2.2.2 255.255.255.255
 ipv6 address 1125:2:2:2::2/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.1.2.2 255.255.255.0
 ipv6 address 1125:1:2::2/64
!
interface GigabitEthernet0/0/0/1
 vrf A
 ipv4 address 10.10.30.2 255.255.255.0
 ipv6 address 1125:1010:30::2/64
!
route-policy PASS
  pass
end-policy
!
router isis AS1
 apply-group CCIE-ISIS
 net 49.0001.0000.0000.0002.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 1
 bgp router-id 2.2.2.2
 address-family ipv4 unicast
 !
 address-family vpnv4 unicast
 !
 address-family ipv6 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 1.1.1.1
  remote-as 1
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:1:1:1::1
  remote-as 1
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf A
  rd 1:2
  address-family ipv4 unicast
  !
  address-family ipv6 unicast
  !
  neighbor 10.10.30.3
   remote-as 2
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:30::3
   remote-as 2
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
mpls oam
!
mpls ldp
 router-id 2.2.2.2
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
c_N3のconfig
hostname c_N3
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf B
 rd 2:3
 address-family ipv4 unicast
  import route-target
   200:1
  !
  export route-target
   100:1
  !
 !
 address-family ipv6 unicast
  import route-target
   400:2
  !
  export route-target
   300:2
  !
 !
!
interface Loopback0
 ipv4 address 3.3.3.3 255.255.255.255
 ipv6 address 1125:3:3:3::3/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.3.4.3 255.255.255.0
 ipv6 address 1125:3:4::3/64
!
interface GigabitEthernet0/0/0/1
 vrf B
 ipv4 address 10.10.30.3 255.255.255.0
 ipv6 address 1125:1010:30::3/64
!
route-policy PASS
  pass
end-policy
!
router isis AS2
 apply-group CCIE-ISIS
 net 49.0002.0000.0000.0003.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 2
 bgp router-id 3.3.3.3
 address-family ipv4 unicast
 !
 address-family vpnv4 unicast
 !
 address-family ipv6 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 4.4.4.4
  remote-as 2
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:4:4:4::4
  remote-as 2
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf B
  rd 2:3
  address-family ipv4 unicast
  !
  address-family ipv6 unicast
  !
  neighbor 10.10.30.2
   remote-as 1
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:30::2
   remote-as 1
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
mpls oam
!
mpls ldp
 router-id 3.3.3.3
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
c_N4のconfig
hostname c_N4
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf B
 rd 2:4
 address-family ipv4 unicast
  import route-target
   100:1
  !
  export route-target
   200:1
  !
 !
 address-family ipv6 unicast
  import route-target
   300:2
  !
  export route-target
   400:2
  !
 !
!
interface Loopback0
 ipv4 address 4.4.4.4 255.255.255.255
 ipv6 address 1125:4:4:4::4/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.3.4.4 255.255.255.0
 ipv6 address 1125:3:4::4/64
!
interface GigabitEthernet0/0/0/1
 vrf B
 ipv4 address 10.10.80.1 255.255.255.0
 ipv6 address 1125:1010:80::1/64
!
route-policy PASS
  pass
end-policy
!
router isis AS2
 apply-group CCIE-ISIS
 net 49.0002.0000.0000.0004.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 2
 bgp router-id 4.4.4.4
 address-family ipv4 unicast
 !
 address-family vpnv4 unicast
 !
 address-family ipv6 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 3.3.3.3
  remote-as 2
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:3:3:3::3
  remote-as 2
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf B
  rd 2:4
  address-family ipv4 unicast
   redistribute connected
  !
  address-family ipv6 unicast
   redistribute connected
  !
  neighbor 10.10.80.2
   remote-as 200
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:80::2
   remote-as 200
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
mpls oam
!
mpls ldp
 router-id 4.4.4.4
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
c_CE1のconfig
hostname c_CE1
!
no ip domain lookup
!
ipv6 unicast-routing
!
interface Loopback0
 ip address 100.100.100.100 255.255.255.255
 ipv6 address 1125:100:100:100::100/128
!
interface GigabitEthernet1
 ip address 10.10.20.2 255.255.255.0
 ipv6 address 1125:1010:20::2/64
!
!
router bgp 100
 bgp router-id 100.100.100.100
 bgp log-neighbor-changes
 no bgp default ipv4-unicast
 neighbor 10.10.20.1 remote-as 1
 neighbor 1125:1010:20::1 remote-as 1
 !
 address-family ipv4
  network 100.100.100.100 mask 255.255.255.255
  neighbor 10.10.20.1 activate
 exit-address-family
 !
 address-family ipv6
  network 1125:100:100:100::100/128
  neighbor 1125:1010:20::1 activate
 exit-address-family
!
end
c_CE2のconfig
hostname c_CE2
!
no ip domain lookup
!
ipv6 unicast-routing
!
interface Loopback0
 ip address 200.200.200.200 255.255.255.255
 ipv6 address 1125:200:200:200::200/128
!
interface GigabitEthernet1
 ip address 10.10.80.2 255.255.255.0
 ipv6 address 1125:1010:80::2/64
!
!
router bgp 200
 bgp router-id 200.200.200.200
 bgp log-neighbor-changes
 no bgp default ipv4-unicast
 neighbor 10.10.80.1 remote-as 2
 neighbor 1125:1010:80::1 remote-as 2
 !
 address-family ipv4
  network 200.200.200.200 mask 255.255.255.255
  neighbor 10.10.80.1 activate
 exit-address-family
 !
 address-family ipv6
  network 1125:200:200:200::200/128
  neighbor 1125:1010:80::1 activate
 exit-address-family
!
end
4. Peering 確認
c_CE1-c_N1(CE-PE)のPeering:CEルータからの確認
c_CE1#show bgp all neighbors | i BGP|For address family
For address family: IPv4 Unicast
BGP neighbor is 10.10.20.1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 05:54:33
  Last reset 05:54:40, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Unicast
BGP neighbor is 1125:1010:20::1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 05:54:23
  Last reset 05:54:40, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv4 Multicast
For address family: L2VPN E-VPN
For address family: MVPNv4 Unicast
For address family: MVPNv6 Unicast
For address family: IPv4 Label-Unicast
BGP neighbor is 10.10.20.1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 05:54:33
  Last reset 05:54:40, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Label-Unicast
BGP neighbor is 1125:1010:20::1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 05:54:23
  Last reset 05:54:40, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
c_CE1#
c_CE1-c_N1(CE-PE)のPeering:PEルータからの確認
RP/0/RP0/CPU0:c_N1#show bgp vrf A neighbors | i "BGP|For Address Family"
Sat Jan 21 07:42:06.424 UTC
BGP neighbor is 10.10.20.2, vrf A
  BGP state = Established, up for 06:05:08
 For Address Family: IPv4 Unicast
  BGP neighbor version 158
  Last reset 06:05:14, due to BGP Notification received: administrative reset
BGP neighbor is 1125:1010:20::2, vrf A
  BGP state = Established, up for 06:04:57
 For Address Family: IPv6 Unicast
  BGP neighbor version 158
  Last reset 06:05:14, due to BGP Notification received: administrative reset
RP/0/RP0/CPU0:c_N1#
c_N1-c_N2(PE-ASBR)のPeering:PEルータからの確認
RP/0/RP0/CPU0:c_N1#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 21 07:35:51.934 UTC
BGP neighbor is 2.2.2.2
  BGP state = Established, up for 03:33:12
 For Address Family: VPNv4 Unicast
  BGP neighbor version 158
  Last reset 03:33:35, due to BGP Notification received: configuration change
BGP neighbor is 1125:2:2:2::2
  BGP state = Established, up for 03:33:13
 For Address Family: VPNv6 Unicast
  BGP neighbor version 158
  Last reset 03:33:35, due to BGP Notification received: configuration change
RP/0/RP0/CPU0:c_N1#
c_N1-c_N2(PE-ASBR)のPeering:ASBRルータからの確認
RP/0/RP0/CPU0:c_N2#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 21 07:36:55.940 UTC
BGP neighbor is 1.1.1.1
  BGP state = Established, up for 03:34:15
 For Address Family: VPNv4 Unicast
  BGP neighbor version 71
BGP neighbor is 1125:1:1:1::1
  BGP state = Established, up for 03:34:16
 For Address Family: VPNv6 Unicast
  BGP neighbor version 71
RP/0/RP0/CPU0:c_N2#
c_N2-c_N3(ASBR-ASBR)のPeering:AS1のASBRルータからの確認
RP/0/RP0/CPU0:c_N2#show bgp vrf A neighbors | i "BGP|For Address Family"
Sat Jan 21 07:44:23.763 UTC
BGP neighbor is 10.10.30.3, vrf A
  BGP state = Established, up for 6d02h
 For Address Family: IPv4 Unicast
  BGP neighbor version 71
BGP neighbor is 1125:1010:30::3, vrf A
  BGP state = Established, up for 6d02h
 For Address Family: IPv6 Unicast
  BGP neighbor version 71
RP/0/RP0/CPU0:c_N2#
c_N2-c_N3(ASBR-ASBR)のPeering:AS2のASBRルータからの確認
RP/0/RP0/CPU0:c_N3#show bgp vrf B neighbors | i "BGP|For Address Family"
Sat Jan 21 07:46:37.024 UTC
BGP neighbor is 10.10.30.2, vrf B
  BGP state = Established, up for 6d02h
 For Address Family: IPv4 Unicast
  BGP neighbor version 65
BGP neighbor is 1125:1010:30::2, vrf B
  BGP state = Established, up for 6d02h
 For Address Family: IPv6 Unicast
  BGP neighbor version 65
RP/0/RP0/CPU0:c_N3#
c_N3-c_N4(ASBR-PE)のPeering:ASBRルータからの確認
RP/0/RP0/CPU0:c_N3#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 21 07:47:56.818 UTC
BGP neighbor is 4.4.4.4
  BGP state = Established, up for 03:13:07
 For Address Family: VPNv4 Unicast
  BGP neighbor version 65
  Last reset 03:18:42, due to BGP Notification sent: hold time expired
BGP neighbor is 1125:4:4:4::4
  BGP state = Established, up for 03:12:57
 For Address Family: VPNv6 Unicast
  BGP neighbor version 65
  Last reset 03:19:31, due to BGP Notification sent: hold time expired
RP/0/RP0/CPU0:c_N3#
c_N3-c_N4(ASBR-PE)のPeering:PEルータからの確認
RP/0/RP0/CPU0:c_N4#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 21 07:48:37.127 UTC
BGP neighbor is 3.3.3.3
  BGP state = Established, up for 03:13:48
 For Address Family: VPNv4 Unicast
  BGP neighbor version 74
  Last reset 03:19:56, due to BGP Notification sent: hold time expired
BGP neighbor is 1125:3:3:3::3
  BGP state = Established, up for 03:13:38
 For Address Family: VPNv6 Unicast
  BGP neighbor version 78
  Last reset 03:19:56, due to BGP Notification sent: hold time expired
RP/0/RP0/CPU0:c_N4#
c_N4-c_CE2(PE-CE2)のPeering:PEルータからの確認
RP/0/RP0/CPU0:c_N4#show bgp vrf B neighbors | i "BGP|For Address Family"
Sat Jan 21 07:50:32.057 UTC
BGP neighbor is 10.10.80.2, vrf B
  BGP state = Established, up for 6d02h
 For Address Family: IPv4 Unicast
  BGP neighbor version 74
  Last reset 6d02h, due to BGP Notification received: peer in wrong AS
BGP neighbor is 1125:1010:80::2, vrf B
  BGP state = Established, up for 6d02h
 For Address Family: IPv6 Unicast
  BGP neighbor version 78
  Last reset 6d02h, due to BGP Notification received: peer in wrong AS
RP/0/RP0/CPU0:c_N4#
c_N4-c_CE2(PE-CE2)のPeering:CEルータからの確認
c_CE2#show bgp all neighbors | i BGP|For address family
For address family: IPv4 Unicast
BGP neighbor is 10.10.80.1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 6d02h
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Unicast
BGP neighbor is 1125:1010:80::1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 6d02h
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv4 Multicast
For address family: L2VPN E-VPN
For address family: MVPNv4 Unicast
For address family: MVPNv6 Unicast
For address family: IPv4 Label-Unicast
BGP neighbor is 10.10.80.1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 6d02h
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Label-Unicast
BGP neighbor is 1125:1010:80::1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 6d02h
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
c_CE2#
ここで一旦BGPの状態をまとめます。

BGPは想定通りにestablishしていますが、Inter-AS Option A ではVRFのRTが重要です。
2. Topology で触れましたが、RTが適切でないとルーティング情報は問題なさそうに見えますがend-to-endで疎通できません。
以降はRTが適切になっている前提で説明していきます。
5. vpnv4 確認
疎通確認とLFIBの確認はこのような感じになりました。
c_CE1#show ip route bgp | b Gate
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
B        10.10.80.0/24 [20/0] via 10.10.20.1, 02:16:35
      200.200.200.0/32 is subnetted, 1 subnets
B        200.200.200.200 [20/0] via 10.10.20.1, 02:16:35
c_CE1#
c_CE1#traceroute 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Tracing the route to 200.200.200.200
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.20.1 [AS 1] 6 msec 2 msec 1 msec
  2 10.1.2.2 [MPLS: Label 24004 Exp 0] 6 msec 3 msec 3 msec
  3 10.10.30.3 4 msec 2 msec 2 msec
  4 10.3.4.4 [MPLS: Label 24002 Exp 0] 7 msec 5 msec 5 msec
  5 10.10.80.2 [AS 2] 6 msec *  12 msec
c_CE1#
c_CE1#ping 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 200.200.200.200, timeout is 2 seconds:
Packet sent with a source address of 100.100.100.100
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 4/5/11 ms
c_CE1#

正直手探りと勘で正解にたどり着いたようなもので、いまいちな理解で少しモヤモヤしていました。
困った時のCisco-Press!
ということで”BGP Design and Implementation ”を参照すると適切な確認コマンドがありました。
www.ciscopress.com
参照箇所:Back-to-Back VRF(Page 462 Chapter10:Multiprotocol BGP and MPLS VPN)
コマンド:show bgp vpnv4 unicast vrf 【VRF name】【route】
コマンドの出力内容を確認すると、CE-PE間のVRFとASBR-ASBR間のVRFが密接に関係することが分かりました。
宛先に到達するためには、RDが何でどのRTを使ってNEXT_HOPは何かが分かります。
そのため、Topology図にある通り各VRFでRTがクロスするようにする必要があります。
c_CE1(CEルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
NEXT_HOP は 10.10.20.1
AS100 -> AS1 -> AS2 -> AS200
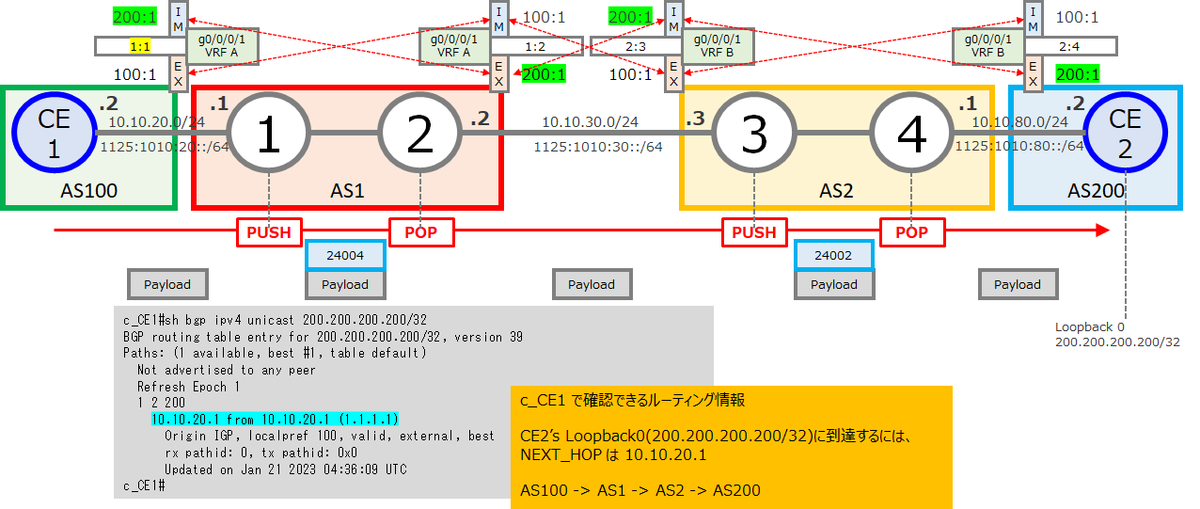
c_N1(PEルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
RD 1:1 で route-target export 200:1 を使う
NEXT_HOP は 2.2.2.2(Label 24004)

c_N2(ASBRルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
Local Label 24004
RD 1:2 で route-target export 200:1 を使う
NEXT_HOP は 10.10.30.3
このVRFをAdvertiseしているのは、1.1.1.1 つまり、c_N1である。
ASBRのコマンド出力でVRFのRTが一続きに関係しているのが分かりやすいと思います。

c_N3(ASBRルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
RD 2:3 で route-target export 200:1 を使う
NEXT_HOP は 4.4.4.4(Label 24002)

c_N4(PEルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
Local Label 24002
RD 2:4 で route-target export 200:1 を使う
NEXT_HOP は 10.10.80.2

同様にIPv6も確認します。
6. vpnv6 確認
疎通確認とLFIBの確認はこのような感じになりました。
c_CE1#show ipv6 route bgp
IPv6 Routing Table - default - 6 entries
Codes: C - Connected, L - Local, S - Static, U - Per-user Static route
       B - BGP, R - RIP, H - NHRP, I1 - ISIS L1
       I2 - ISIS L2, IA - ISIS interarea, IS - ISIS summary, D - EIGRP
       EX - EIGRP external, ND - ND Default, NDp - ND Prefix, DCE - Destination
       NDr - Redirect, RL - RPL, O - OSPF Intra, OI - OSPF Inter
       OE1 - OSPF ext 1, OE2 - OSPF ext 2, ON1 - OSPF NSSA ext 1
       ON2 - OSPF NSSA ext 2, la - LISP alt, lr - LISP site-registrations
       ld - LISP dyn-eid, lA - LISP away, le - LISP extranet-policy
       lp - LISP publications, a - Application, m - OMP
B   1125:200:200:200::200/128 [20/0], tag 1
     via FE80::5200:FF:FE22:4, GigabitEthernet1
B   1125:1010:80::/64 [20/0], tag 1
     via FE80::5200:FF:FE22:4, GigabitEthernet1
c_CE1#
c_CE1#traceroute 1125:200:200:200::200 source 1125:100:100:100::100
Type escape sequence to abort.
Tracing the route to 1125:200:200:200::200

  1 1125:1010:20::1 [AS 1] 3 msec 2 msec 2 msec
  2 1125:1:2::2 [MPLS: Label 24005 Exp 0] 4 msec 3 msec 3 msec
  3 1125:1010:30::3 7 msec 6 msec 2 msec
  4 1125:3:4::4 [MPLS: Label 24003 Exp 0] 8 msec 5 msec 6 msec
  5 1125:1010:80::2 [AS 2] 6 msec 4 msec 5 msec
c_CE1#
c_CE1#ping ipv6 1125:200:200:200::200 source 1125:100:100:100::100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 1125:200:200:200::200, timeout is 2 seconds:
Packet sent with a source address of 1125:100:100:100::100
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 3/4/7 ms
c_CE1#

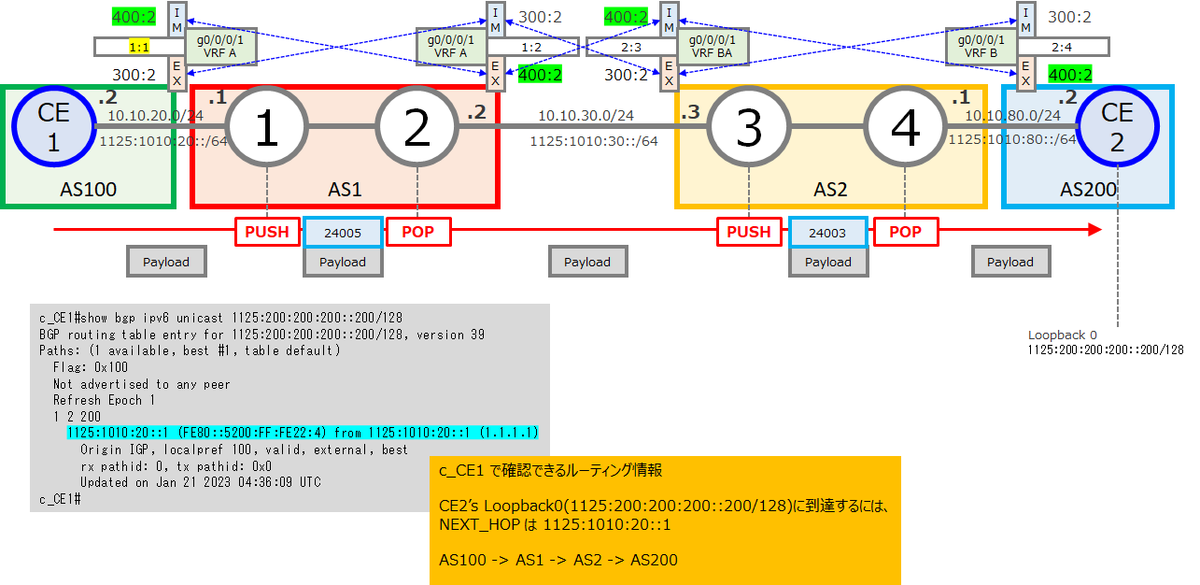
c_CE1(CEルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
NEXT_HOP は 1125:1010:20::1
AS100 -> AS1 -> AS2 -> AS200
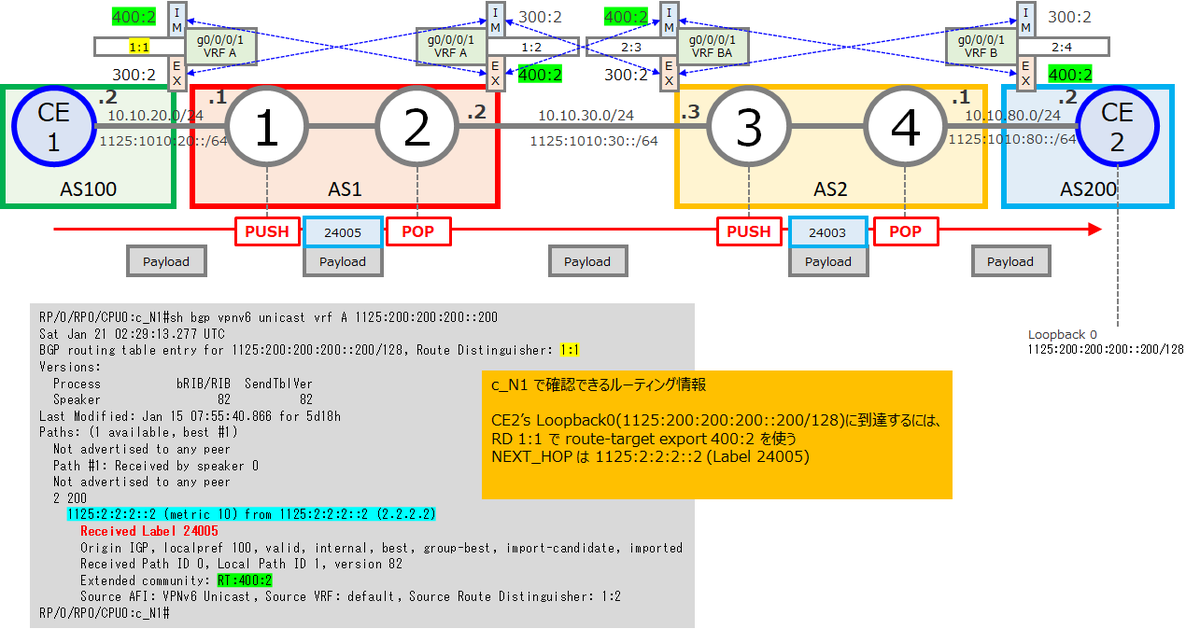
c_N1(PEルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
RD 1:1 で route-target export 400:2 を使う
NEXT_HOP は 1125:2:2:2::2 (Label 24005)
c_N2(ASBRルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
Local Label 24005
RD 1:2 で route-target export 400:2 を使う
NEXT_HOP は 1125:1010:30::3
このVRFをAdvertiseしているのは、1125:1:1:1::1 つまり、c_N1である。

c_N3(ASBRルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
RD 2:3 で route-target export 400:2 を使う
NEXT_HOP は 1125:4:4:4::4 (Label 24003)

c_N4(PEルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
RD 2:3 で route-target export 400:2 を使う
NEXT_HOP は 1125:4:4:4::4 (Label 24003)

次回は、Inter-AS Option B について記事を書きます。
最後までお読みいただきありがとうございました!
