CCIE lab対策(2.4.b Inter-AS L3VPN)その2 Inter-AS option B
Inter-AS option B (IOS-XR)が理解できたので自分のメモ用にアウトプットします。
- 1. Inter-AS Option B とは
- 2. Topology
- 3. Config
- 4. Peering 確認
- 5. 重要なポイント
- 6. vpnv4 確認
- 7. vpnv6 確認
- 8. 参考URL
1. Inter-AS Option B とは
Inter-AS Option B とは、Inter-AS Link で VPN を使って end-to-end の通信を行う方式です。
Inter-AS Option A と異なり、Inter-AS Link で VRF-lite を使うことが無いので少し楽です。
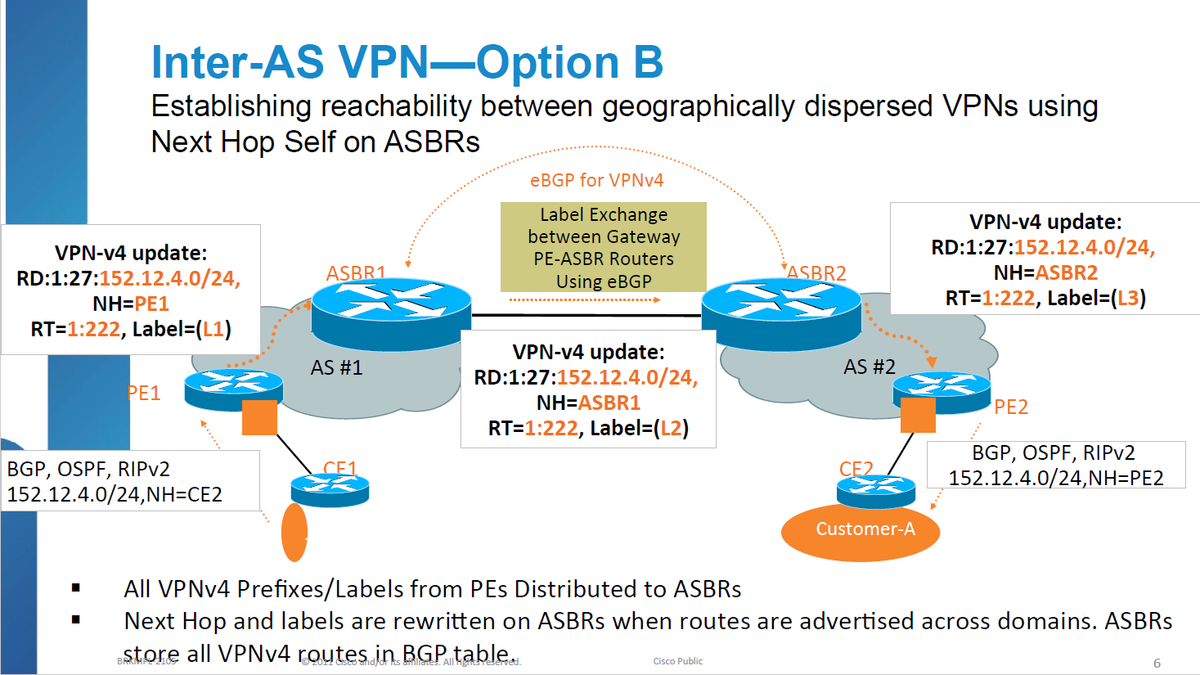
リンク先のドキュメントは大変素晴らしく、今回もこのドキュメントのおかげで構築できたと言っても過言ではありません。
https://nsrc.org/workshops/2015/apricot2015/raw-attachment/wiki/Track3MPLS/9-Apriot_2015_Inter-AS.2.pdf
ポイントとしては、以下の3点です。
① ASBR-PE間で next-hop-self を定義すること
② ASBRで retain route-target all を定義すること
③ ASBR-ASBR間で static route を定義すること
2. Topology
CE-PE-ASBR-ASBR-PE-CE を含めた最小構成としました。

IOS-XR version
RP/0/RP0/CPU0:d_N1#show version
Sat Jan 28 04:21:07.272 UTC
Cisco IOS XR Software, Version 7.4.1
Copyright (c) 2013-2021 by Cisco Systems, Inc.

Build Information:
 Built By     : ingunawa
 Built On     : Wed Aug  4 04:18:28 PDT 2021
 Built Host   : iox-ucs-012
 Workspace    : /auto/srcarchive17/prod/7.4.1/xrv9k/ws
 Version      : 7.4.1
 Location     : /opt/cisco/XR/packages/
 Label        : 7.4.1-0

cisco IOS-XRv 9000 () processor
System uptime is 1 week 5 days 19 hours 20 minutes

RP/0/RP0/CPU0:d_N1#
IOS-XE version
d_CE1#show version
Cisco IOS XE Software, Version 17.03.04a
3. Config
d_N1のconfig
hostname d_N1
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf A
 rd 1:1
 address-family ipv4 unicast
  import route-target
   200:1
  !
  export route-target
   100:1
  !
 !
 address-family ipv6 unicast
  import route-target
   400:2
  !
  export route-target
   300:2
  !
 !
!
!
interface Loopback0
 ipv4 address 1.1.1.1 255.255.255.255
 ipv6 address 1125:1:1:1::1/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.1.2.1 255.255.255.0
 ipv6 address 1125:1:2::1/64
!
interface GigabitEthernet0/0/0/1
 vrf A
 ipv4 address 10.10.20.1 255.255.255.0
 ipv6 address 1125:1010:20::1/64
!
!
route-policy PASS
  pass
end-policy
!
router isis AS1
 apply-group CCIE-ISIS
 net 49.0001.0000.0000.0001.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 1
 bgp router-id 1.1.1.1
 address-family vpnv4 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 2.2.2.2
  remote-as 1
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:2:2:2::2
  remote-as 1
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf A
  rd 1:1
  address-family ipv4 unicast
   redistribute connected
  !
  address-family ipv6 unicast
   redistribute connected
  !
  neighbor 10.10.20.2
   remote-as 100
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:20::2
   remote-as 100
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
mpls oam
!
mpls ldp
 router-id 1.1.1.1
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
d_N2のconfig
hostname d_N2
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
interface Loopback0
 ipv4 address 2.2.2.2 255.255.255.255
 ipv6 address 1125:2:2:2::2/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.1.2.2 255.255.255.0
 ipv6 address 1125:1:2::2/64
!
interface GigabitEthernet0/0/0/1
 ipv4 address 10.10.30.2 255.255.255.0
 ipv6 address 1125:1010:30::2/64
!
route-policy PASS
  pass
end-policy
!
router static
 address-family ipv4 unicast
  10.10.30.3/32 GigabitEthernet0/0/0/1
 !
 address-family ipv6 unicast
  1125:1010:30::3/128 GigabitEthernet0/0/0/1
 !
!
router isis AS1
 apply-group CCIE-ISIS
 net 49.0001.0000.0000.0002.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 1
 bgp router-id 2.2.2.2
 address-family vpnv4 unicast
  retain route-target all
 !
 address-family vpnv6 unicast
  retain route-target all
 !
 neighbor 1.1.1.1
  remote-as 1
  update-source Loopback0
  address-family vpnv4 unicast
   next-hop-self
  !
 !
 neighbor 10.10.30.3
  remote-as 2
  address-family vpnv4 unicast
   route-policy PASS in
   route-policy PASS out
  !
 !
 neighbor 1125:1:1:1::1
  remote-as 1
  update-source Loopback0
  address-family vpnv6 unicast
   next-hop-self
  !
 !
 neighbor 1125:1010:30::3
  remote-as 2
  address-family vpnv6 unicast
   route-policy PASS in
   route-policy PASS out
  !
 !
!
mpls oam
!
mpls ldp
 router-id 2.2.2.2
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
d_N3のconfig
hostname d_N3
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
interface Loopback0
 ipv4 address 3.3.3.3 255.255.255.255
 ipv6 address 1125:3:3:3::3/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.3.4.3 255.255.255.0
 ipv6 address 1125:3:4::3/64
!
interface GigabitEthernet0/0/0/1
 ipv4 address 10.10.30.3 255.255.255.0
 ipv6 address 1125:1010:30::3/64
!
route-policy PASS
  pass
end-policy
!
router static
 address-family ipv4 unicast
  10.10.30.2/32 GigabitEthernet0/0/0/1
 !
 address-family ipv6 unicast
  1125:1010:30::2/128 GigabitEthernet0/0/0/1
 !
!
router isis AS2
 apply-group CCIE-ISIS
 net 49.0002.0000.0000.0003.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 2
 bgp router-id 3.3.3.3
 address-family vpnv4 unicast
  retain route-target all
 !
 address-family vpnv6 unicast
  retain route-target all
 !
 neighbor 4.4.4.4
  remote-as 2
  update-source Loopback0
  address-family vpnv4 unicast
   next-hop-self
  !
 !
 neighbor 10.10.30.2
  remote-as 1
  address-family vpnv4 unicast
   route-policy PASS in
   route-policy PASS out
  !
 !
 neighbor 1125:4:4:4::4
  remote-as 2
  update-source Loopback0
  address-family vpnv6 unicast
   next-hop-self
  !
 !
 neighbor 1125:1010:30::2
  remote-as 1
  address-family vpnv6 unicast
   route-policy PASS in
   route-policy PASS out
  !
 !
!
!
mpls oam
!
mpls ldp
 router-id 3.3.3.3
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
d_N4のconfig
hostname d_N4
group CCIE-ISIS
 router isis '.*'
  is-type level-2-only
  address-family ipv4 unicast
   metric-style wide
   mpls ldp auto-config
  !
  address-family ipv6 unicast
   single-topology
  !
  interface 'Gi.*'
   point-to-point
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
  interface 'Loopback.*'
   passive
   address-family ipv4 unicast
   !
   address-family ipv6 unicast
   !
  !
 !
end-group
!
vrf B
 rd 2:4
 address-family ipv4 unicast
  import route-target
   100:1
  !
  export route-target
   200:1
  !
 !
 address-family ipv6 unicast
  import route-target
   300:2
  !
  export route-target
   400:2
  !
 !
!
interface Loopback0
 ipv4 address 4.4.4.4 255.255.255.255
 ipv6 address 1125:4:4:4::4/128
!
interface GigabitEthernet0/0/0/0
 ipv4 address 10.3.4.4 255.255.255.0
 ipv6 address 1125:3:4::4/64
!
interface GigabitEthernet0/0/0/1
 vrf B
 ipv4 address 10.10.80.1 255.255.255.0
 ipv6 address 1125:1010:80::1/64
!
!
route-policy PASS
  pass
end-policy
!
router isis AS2
 apply-group CCIE-ISIS
 net 49.0002.0000.0000.0004.00
 interface Loopback0
 !
 interface GigabitEthernet0/0/0/0
 !
!
router bgp 2
 bgp router-id 4.4.4.4
 address-family vpnv4 unicast
 !
 address-family vpnv6 unicast
 !
 neighbor 3.3.3.3
  remote-as 2
  update-source Loopback0
  address-family vpnv4 unicast
  !
 !
 neighbor 1125:3:3:3::3
  remote-as 2
  update-source Loopback0
  address-family vpnv6 unicast
  !
 !
 vrf B
  rd 2:4
  address-family ipv4 unicast
   redistribute connected
  !
  address-family ipv6 unicast
   redistribute connected
  !
  neighbor 10.10.80.2
   remote-as 200
   address-family ipv4 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
  neighbor 1125:1010:80::2
   remote-as 200
   address-family ipv6 unicast
    route-policy PASS in
    route-policy PASS out
   !
  !
 !
!
!
mpls oam
!
mpls ldp
 router-id 4.4.4.4
 address-family ipv6
 !
 interface GigabitEthernet0/0/0/0
  address-family ipv6
  !
 !
!
end
d_CE1のconfig
hostname d_CE1
!
no ip domain lookup
!
ipv6 unicast-routing
!
!
interface Loopback0
 ip address 100.100.100.100 255.255.255.255
 ipv6 address 1125:100:100:100::100/128
!
interface GigabitEthernet1
 ip address 10.10.20.2 255.255.255.0
 ipv6 address 1125:1010:20::2/64
!
!
router bgp 100
 bgp router-id 100.100.100.100
 bgp log-neighbor-changes
 no bgp default ipv4-unicast
 neighbor 10.10.20.1 remote-as 1
 neighbor 1125:1010:20::1 remote-as 1
 !
 address-family ipv4
  network 100.100.100.100 mask 255.255.255.255
  neighbor 10.10.20.1 activate
 exit-address-family
 !
 address-family ipv6
  network 1125:100:100:100::100/128
  neighbor 1125:1010:20::1 activate
 exit-address-family
!
end
d_CE2のconfig
hostname d_CE2
!
no ip domain lookup
!
ipv6 unicast-routing
!
interface Loopback0
 ip address 200.200.200.200 255.255.255.255
 ipv6 address 1125:200:200:200::200/128
!
interface GigabitEthernet1
 ip address 10.10.80.2 255.255.255.0
 ipv6 address 1125:1010:80::2/64
!
!
router bgp 200
 bgp router-id 200.200.200.200
 bgp log-neighbor-changes
 no bgp default ipv4-unicast
 neighbor 10.10.80.1 remote-as 2
 neighbor 1125:1010:80::1 remote-as 2
 !
 address-family ipv4
  network 200.200.200.200 mask 255.255.255.255
  neighbor 10.10.80.1 activate
 exit-address-family
 !
 address-family ipv6
  network 1125:200:200:200::200/128
  neighbor 1125:1010:80::1 activate
 exit-address-family
!
end
4. Peering 確認
d_CE1-d_N1(CE-PE)のPeering:CEルータからの確認
d_CE1#show bgp all neighbors | i BGP|For address family
For address family: IPv4 Unicast
BGP neighbor is 10.10.20.1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 1w4d
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Unicast
BGP neighbor is 1125:1010:20::1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 1w4d
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv4 Multicast
For address family: L2VPN E-VPN
For address family: MVPNv4 Unicast
For address family: MVPNv6 Unicast
For address family: IPv4 Label-Unicast
BGP neighbor is 10.10.20.1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 1w4d
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Label-Unicast
BGP neighbor is 1125:1010:20::1,  remote AS 1, external link
  BGP version 4, remote router ID 1.1.1.1
  BGP state = Established, up for 1w4d
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
d_CE1#
d_CE1-d_N1(CE-PE)のPeering:PEルータからの確認
RP/0/RP0/CPU0:d_N1#show bgp vrf A neighbors | i "BGP|For Address Family"
Sat Jan 28 04:49:15.240 UTC
BGP neighbor is 10.10.20.2, vrf A
  BGP state = Established, up for 1w4d
 For Address Family: IPv4 Unicast
  BGP neighbor version 114
BGP neighbor is 1125:1010:20::2, vrf A
  BGP state = Established, up for 1w4d
 For Address Family: IPv6 Unicast
  BGP neighbor version 82
RP/0/RP0/CPU0:d_N1#
d_N1-d_N2(PE-ASBR)のPeering:PEルータからの確認
RP/0/RP0/CPU0:d_N1#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 28 04:49:34.659 UTC
BGP neighbor is 2.2.2.2
  BGP state = Established, up for 01:53:47
 For Address Family: VPNv4 Unicast
  BGP neighbor version 114
  Last reset 01:54:08, due to BGP Notification received: configuration change
BGP neighbor is 1125:2:2:2::2
  BGP state = Established, up for 01:52:55
 For Address Family: VPNv6 Unicast
  BGP neighbor version 82
  Last reset 01:53:27, due to BGP Notification received: configuration change
RP/0/RP0/CPU0:d_N1#
d_N1-d_N2(PE-ASBR)のPeering:ASBRルータからの確認 d_N2-d_N3(ASBR-ASBR)のPeering:AS1のASBRルータからの確認
RP/0/RP0/CPU0:d_N2#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 28 04:49:52.534 UTC
BGP neighbor is 1.1.1.1
  BGP state = Established, up for 01:54:04
 For Address Family: VPNv4 Unicast
  BGP neighbor version 73
BGP neighbor is 10.10.30.3
  BGP state = Established, up for 00:40:41
 For Address Family: VPNv4 Unicast
  BGP neighbor version 73
  Last reset 00:41:22, due to BGP Notification received: configuration change
BGP neighbor is 1125:1:1:1::1
  BGP state = Established, up for 01:53:13
 For Address Family: VPNv6 Unicast
  BGP neighbor version 61
BGP neighbor is 1125:1010:30::3
  BGP state = Established, up for 00:33:36
 For Address Family: VPNv6 Unicast
  BGP neighbor version 61
RP/0/RP0/CPU0:d_N2#
d_N2-d_N3(ASBR-ASBR)のPeering:AS2のASBRルータからの確認
d_N3-d_N4(ASBR-PE)のPeering:ASBRルータからの確認
RP/0/RP0/CPU0:d_N3#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 28 04:51:26.075 UTC
BGP neighbor is 4.4.4.4
  BGP state = Established, up for 01:39:33
 For Address Family: VPNv4 Unicast
  BGP neighbor version 75
  Last reset 01:40:04, due to BGP Notification received: configuration change
BGP neighbor is 10.10.30.2
  BGP state = Established, up for 00:42:13
 For Address Family: VPNv4 Unicast
  BGP neighbor version 75
BGP neighbor is 1125:4:4:4::4
  BGP state = Established, up for 00:35:37
 For Address Family: VPNv6 Unicast
  BGP neighbor version 59
BGP neighbor is 1125:1010:30::2
  BGP state = Established, up for 00:35:08
 For Address Family: VPNv6 Unicast
  BGP neighbor version 59
RP/0/RP0/CPU0:d_N3#
d_N3-d_N4(ASBR-PE)のPeering:PEルータからの確認
RP/0/RP0/CPU0:d_N4#show bgp all all neighbors | i "BGP|For Address Family"
Sat Jan 28 04:51:45.366 UTC
BGP neighbor is 3.3.3.3
  BGP state = Established, up for 01:39:54
 For Address Family: VPNv4 Unicast
  BGP neighbor version 110
BGP neighbor is 1125:3:3:3::3
  BGP state = Established, up for 00:35:58
 For Address Family: VPNv6 Unicast
  BGP neighbor version 78
RP/0/RP0/CPU0:d_N4#
d_N4-d_CE2(PE-CE2)のPeering:PEルータからの確認
RP/0/RP0/CPU0:d_N4#show bgp vrf B neighbors | i "BGP|For Address Family"
Sat Jan 28 04:51:57.468 UTC
BGP neighbor is 10.10.80.2, vrf B
  BGP state = Established, up for 02:48:34
 For Address Family: IPv4 Unicast
  BGP neighbor version 110
  Last reset 02:48:48, due to BGP Notification received: administrative reset
BGP neighbor is 1125:1010:80::2, vrf B
  BGP state = Established, up for 02:48:39
 For Address Family: IPv6 Unicast
  BGP neighbor version 78
  Last reset 02:48:48, due to BGP Notification received: administrative reset
RP/0/RP0/CPU0:d_N4#
d_N4-d_CE2(PE-CE2)のPeering:CEルータからの確認
d_CE2#show bgp all neighbors | i BGP|For address family
For address family: IPv4 Unicast
BGP neighbor is 10.10.80.1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 02:51:49
  Last reset 02:52:03, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Unicast
BGP neighbor is 1125:1010:80::1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 02:51:55
  Last reset 02:52:03, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv4 Multicast
For address family: L2VPN E-VPN
For address family: MVPNv4 Unicast
For address family: MVPNv6 Unicast
For address family: IPv4 Label-Unicast
BGP neighbor is 10.10.80.1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 02:51:49
  Last reset 02:52:03, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
For address family: IPv6 Label-Unicast
BGP neighbor is 1125:1010:80::1,  remote AS 2, external link
  BGP version 4, remote router ID 4.4.4.4
  BGP state = Established, up for 02:51:55
  Last reset 02:52:03, due to BGP protocol initialization
  External BGP neighbor configured for connected checks (single-hop no-disable-connected-check)
d_CE2#
ここで一旦BGPの状態をまとめます。

BGPは想定通りにestablishしていますが果たして確認は十分でしょうか。
冒頭で触れたとおり、重要なポイントをクリアしないとend-to-endで疎通できません。
5. 重要なポイント
5.1 next-hop-self
とても大事なことを言います。
大事な事
— やすお (@chimay_wh) 2023年1月8日
iBGPはnext-hopを変えない

iBGPは NEXT_HOP を変更しません。
d_N2 で『 iBGP に NEXT_HOP を自分のアドレスに変更して advertise する!』必要があります。
ASBR-PE間で next-hop-self を定義にすること
router bgp 1 neighbor 1.1.1.1 address-family vpnv4 unicast next-hop-self
router bgp 1 neighbor 1125:1:1:1::1 address-family vpnv6 unicast next-hop-self
(。´・ω・)ん? NEXT_HOP 変更したのに状況が変わらない!
RP/0/RP0/CPU0:d_N1#show route | begin Gate
Sat Jan 28 05:57:49.444 UTC
Gateway of last resort is not set

L    1.1.1.1/32 is directly connected, 1w4d, Loopback0
i L2 2.2.2.2/32 [115/10] via 10.1.2.2, 1w1d, GigabitEthernet0/0/0/0
C    10.1.2.0/24 is directly connected, 1w4d, GigabitEthernet0/0/0/0
L    10.1.2.1/32 is directly connected, 1w4d, GigabitEthernet0/0/0/0
L    127.0.0.0/8 [0/0] via 0.0.0.0, 1w4d
RP/0/RP0/CPU0:d_N1#
RP/0/RP0/CPU0:d_N1#show route vrf A | b Gate
Sat Jan 28 05:57:53.456 UTC
Gateway of last resort is not set

C    10.10.20.0/24 is directly connected, 1w4d, GigabitEthernet0/0/0/1
L    10.10.20.1/32 is directly connected, 1w4d, GigabitEthernet0/0/0/1
B    100.100.100.100/32 [20/0] via 10.10.20.2, 1w4d
RP/0/RP0/CPU0:d_N1#
これは次のポイントをクリアすることで解決します。
5.2 retain route-target all
CCOにしっかり書いてありました。
www.cisco.com
On the ASBR device "no bgp default route-target filter" for IOS and "retain route-target all" for the IOS-XR has been configured. This is important as the ABBR devices are not route-reflectors and they do not have any vrfs with RT (route target) configured, so they will implicitly drop the routing update sent to them from the route-reflectors. This is an expected behaviour as IOS and IOS-XR tend optimize the routing table information and drop the updates for those vrfs with RTs which are not locally configured.
ASBR には route-target を定義したVRFがないので暗黙的に route-target を破棄してしまう仕様とのことです。
これは IOS-XE コマンドでは、"no bgp default route-target filter"
IOS-XR コマンドでは、"retain route-target all" で解決できます。
RTを全部残す!直訳すると覚えやすいです。
ということで、双方のASBRでRTを全部残してやります。
RP/0/RP0/CPU0:d_N2(config)#
router bgp 1 address-family vpnv4 unicast retain route-target all
router bgp 1 address-family vpnv6 unicast retain route-target all
RP/0/RP0/CPU0:d_N2(config)#commit
RP/0/RP0/CPU0:d_N3(config)#
router bgp 2 address-family vpnv4 unicast retain route-target all
router bgp 2 address-family vpnv6 unicast retain route-target all
RP/0/RP0/CPU0:d_N3(config)#commit

すると、AS200 のCE2's Loopback の prefix が流れ込んできました。
RP/0/RP0/CPU0:d_N1#show route | begin Gate
Sat Jan 28 06:00:33.857 UTC
Gateway of last resort is not set

L    1.1.1.1/32 is directly connected, 1w4d, Loopback0
i L2 2.2.2.2/32 [115/10] via 10.1.2.2, 1w1d, GigabitEthernet0/0/0/0
C    10.1.2.0/24 is directly connected, 1w4d, GigabitEthernet0/0/0/0
L    10.1.2.1/32 is directly connected, 1w4d, GigabitEthernet0/0/0/0
L    127.0.0.0/8 [0/0] via 0.0.0.0, 1w4d
RP/0/RP0/CPU0:d_N1#
RP/0/RP0/CPU0:d_N1#show route vrf A | b Gate
Sat Jan 28 06:00:36.993 UTC
Gateway of last resort is not set

C    10.10.20.0/24 is directly connected, 1w4d, GigabitEthernet0/0/0/1
L    10.10.20.1/32 is directly connected, 1w4d, GigabitEthernet0/0/0/1
B    10.10.80.0/24 [200/0] via 2.2.2.2 (nexthop in vrf default), 00:00:46
B    100.100.100.100/32 [20/0] via 10.10.20.2, 1w4d
B    200.200.200.200/32 [200/0] via 2.2.2.2 (nexthop in vrf default), 00:00:46
RP/0/RP0/CPU0:d_N1#
ここまで出来れば当然CEルータにもルーティング情報が届きます。
d_CE1#show ip route bgp | begin Gate
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
B        10.10.80.0/24 [20/0] via 10.10.20.1, 00:30:00
      200.200.200.0/32 is subnetted, 1 subnets
B        200.200.200.200 [20/0] via 10.10.20.1, 00:30:00
d_CE1#
d_CE1#show ipv6 route bgp
IPv6 Routing Table - default - 6 entries
Codes: C - Connected, L - Local, S - Static, U - Per-user Static route
       B - BGP, R - RIP, H - NHRP, I1 - ISIS L1
       I2 - ISIS L2, IA - ISIS interarea, IS - ISIS summary, D - EIGRP
       EX - EIGRP external, ND - ND Default, NDp - ND Prefix, DCE - Destination
       NDr - Redirect, RL - RPL, O - OSPF Intra, OI - OSPF Inter
       OE1 - OSPF ext 1, OE2 - OSPF ext 2, ON1 - OSPF NSSA ext 1
       ON2 - OSPF NSSA ext 2, la - LISP alt, lr - LISP site-registrations
       ld - LISP dyn-eid, lA - LISP away, le - LISP extranet-policy
       lp - LISP publications, a - Application, m - OMP
B   1125:200:200:200::200/128 [20/0], tag 1
     via FE80::5200:FF:FE2B:4, GigabitEthernet1
B   1125:1010:80::/64 [20/0], tag 1
     via FE80::5200:FF:FE2B:4, GigabitEthernet1
d_CE1#
疎通確認してみます。
d_CE1#ping 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 200.200.200.200, timeout is 2 seconds:
Packet sent with a source address of 100.100.100.100
.....
Success rate is 0 percent (0/5)
d_CE1#
d_CE1#ping ipv6 1125:200:200:200::200 source 1125:100:100:100::100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 1125:200:200:200::200, timeout is 2 seconds:
Packet sent with a source address of 1125:100:100:100::100
.....
Success rate is 0 percent (0/5)
d_CE1#
(。´・ω・)ん?疎通できない!ルーティング情報が存在するのに疎通できない!
これは次のポイントをクリアすることで解決します。
5.3 static route
これもCCOにしっかり書いてありました。 www.cisco.com
For IOS-XR over Inter-As link there is a different logic as compared to that of IOS. It is required to configure a static /32 route to ASBR1's interface, so that mpls label is bound for a /32 prefix. If this is not done then control plane will come up but the traffic will not be forwarded.
mpls ラベルが /32 プレフィックス用にバインドされるように、静的 /32 ルートを ASBR のインターフェイスに対して設定する必要があります。
そう言われてみれば確かに何かが足りない!
RP/0/RP0/CPU0:d_N2#sh mpls for
Sat Jan 28 07:02:40.130 UTC
Local  Outgoing    Prefix             Outgoing     Next Hop        Bytes
Label  Label       or ID              Interface                    Switched
------ ----------- ------------------ ------------ --------------- ------------
24000  Pop         1.1.1.1/32         Gi0/0/0/0    10.1.2.1        2503356
24001  Pop         1125:1:1:1::1/128  Gi0/0/0/0    fe80::5200:ff:fe2b:3   \
                                                                   3612868
24002  24000       1:1:10.10.20.0/24               1.1.1.1         0
24003  24003       1:1:100.100.100.100/32   \
                                                   1.1.1.1         0
24004  24000       2:4:10.10.80.0/24               10.10.30.3      0
24005  24003       2:4:200.200.200.200/32   \
                                                   10.10.30.3      0
24006  24001       1:1:1125:100:100:100::100/128   \
                                                   1125:1:1:1::1   0
24007  24002       1:1:1125:1010:20::/64   \
                                                   1125:1:1:1::1   0
24008  24004       2:4:1125:200:200:200::200/128   \
                                                   1125:1010:30::3 0
24009  24005       2:4:1125:1010:80::/64   \
                                                   1125:1010:30::3 0
RP/0/RP0/CPU0:d_N2#
ということで、static route を双方のASBRで定義します。
ちなみにIPv6 の場合は、/128で static route を定義します。
RP/0/RP0/CPU0:d_N2(config)#
router static address-family ipv4 unicast 10.10.30.3/32 GigabitEthernet0/0/0/1
router static address-family ipv6 unicast 1125:1010:30::3/128 GigabitEthernet0/0/0/1
RP/0/RP0/CPU0:d_N2(config)#commit
RP/0/RP0/CPU0:d_N3(config)#
router static address-family ipv4 unicast 10.10.30.2/32 GigabitEthernet0/0/0/1
router static address-family ipv6 unicast 1125:1010:30::2/128 GigabitEthernet0/0/0/1
RP/0/RP0/CPU0:d_N3(config)#commit
Inter-AS Link の Prefix がLFIBに表示されるようになりました。
RP/0/RP0/CPU0:d_N2#show mpls forwarding
Sat Jan 28 07:10:40.143 UTC
Local  Outgoing    Prefix             Outgoing     Next Hop        Bytes
Label  Label       or ID              Interface                    Switched
------ ----------- ------------------ ------------ --------------- ------------
24000  Pop         1.1.1.1/32         Gi0/0/0/0    10.1.2.1        2504148
24001  Pop         1125:1:1:1::1/128  Gi0/0/0/0    fe80::5200:ff:fe2b:3   \
                                                                   3615360
24002  24000       1:1:10.10.20.0/24               1.1.1.1         0
24003  24003       1:1:100.100.100.100/32   \
                                                   1.1.1.1         0
24004  24000       2:4:10.10.80.0/24  Gi0/0/0/1    10.10.30.3      0
24005  24003       2:4:200.200.200.200/32   \
                                      Gi0/0/0/1    10.10.30.3      0
24006  24001       1:1:1125:100:100:100::100/128   \
                                                   1125:1:1:1::1   0
24007  24002       1:1:1125:1010:20::/64   \
                                                   1125:1:1:1::1   0
24008  24004       2:4:1125:200:200:200::200/128   \
                                      Gi0/0/0/1    1125:1010:30::3 0
24009  24005       2:4:1125:1010:80::/64   \
                                      Gi0/0/0/1    1125:1010:30::3 0
24010  Pop         10.10.30.3/32      Gi0/0/0/1    10.10.30.3      0
24011  Pop         1125:1010:30::3/128   \
                                      Gi0/0/0/1    1125:1010:30::3 76
RP/0/RP0/CPU0:d_N2#
冒頭で参考資料を紹介しましたが、最近のOSでは一部不要なコマンドもあるようでした。
Router-Cofiguration mode で、mpls activate
router bgp 1
mpls activate
(!Enables MPLS forwarding onASBR!)
interface
(!Specify ASBR-‐ASBR link!)
address-‐family vpnv4 unicast
これについてもCCOに記載がありました。
www.cisco.com
When the eBGP VPNv4 peering comes up on the ASBR1 (IOS) with the IOS-XR device, automatically the "mpls bgp forwarding" is configured on the Inter-As link. Exchange of the labels with ASBR2, is accomplished not via ldp but via BGP. IOS also automatically adds static /32 route to ASBR2's interface so that mpls label is bound to a /32 route and label switching is properly done.
なるほど最近のIOS-XRでは、BGPで定義しなくていいのか。
— やすお (@chimay_wh) 2023年1月28日
mpls activate
interface gi 0/0/0/x
Inter-AS Link でVPNv4有効にしたら勝手にldpを有効にしてくれる。 pic.twitter.com/wcsBk2Rjie
6. vpnv4 確認
ルーティング情報と疎通確認はこのようになりました。
d_CE1#show ip route bgp | b Gate
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
B        10.10.80.0/24 [20/0] via 10.10.20.1, 02:03:59
      200.200.200.0/32 is subnetted, 1 subnets
B        200.200.200.200 [20/0] via 10.10.20.1, 02:03:59
d_CE1#
d_CE1#ping 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 200.200.200.200, timeout is 2 seconds:
Packet sent with a source address of 100.100.100.100
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 2/3/4 ms
d_CE1#
d_CE1#traceroute 200.200.200.200 source 100.100.100.100
Type escape sequence to abort.
Tracing the route to 200.200.200.200
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.20.1 [AS 1] 4 msec 2 msec 1 msec
  2 10.1.2.2 [MPLS: Label 24005 Exp 0] 14 msec 4 msec 3 msec
  3 10.10.30.3 [MPLS: Label 24003 Exp 0] 4 msec 4 msec 4 msec
  4 10.3.4.4 [MPLS: Label 24003 Exp 0] 4 msec 4 msec 3 msec
  5 10.10.80.2 [AS 2] 12 msec *  5 msec
d_CE1#
d_N1(PEルータ)からCE2’s Loopback0(200.200.200.200/32)に到達するには、
RD 1:1 で route-target 200:1 を使う(ソースのRD 2:4)
NEXT_HOP は 2.2.2.2(Label 24005)

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N2(ASBRルータ)ではこのようになりました。

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N3(ASBRルータ)ではこのようになりました。

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N4(PEルータ)ではこのようになりました。

同様にIPv6も確認します。
7. vpnv6 確認
ルーティング情報と疎通確認はこのようになりました。
d_CE1#show ipv6 route bgp
IPv6 Routing Table - default - 6 entries
Codes: C - Connected, L - Local, S - Static, U - Per-user Static route
       B - BGP, R - RIP, H - NHRP, I1 - ISIS L1
       I2 - ISIS L2, IA - ISIS interarea, IS - ISIS summary, D - EIGRP
       EX - EIGRP external, ND - ND Default, NDp - ND Prefix, DCE - Destination
       NDr - Redirect, RL - RPL, O - OSPF Intra, OI - OSPF Inter
       OE1 - OSPF ext 1, OE2 - OSPF ext 2, ON1 - OSPF NSSA ext 1
       ON2 - OSPF NSSA ext 2, la - LISP alt, lr - LISP site-registrations
       ld - LISP dyn-eid, lA - LISP away, le - LISP extranet-policy
       lp - LISP publications, a - Application, m - OMP
B   1125:200:200:200::200/128 [20/0], tag 1
     via FE80::5200:FF:FE2B:4, GigabitEthernet1
B   1125:1010:80::/64 [20/0], tag 1
     via FE80::5200:FF:FE2B:4, GigabitEthernet1
d_CE1#
d_CE1#ping ipv6 1125:200:200:200::200 source 1125:100:100:100::100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 1125:200:200:200::200, timeout is 2 seconds:
Packet sent with a source address of 1125:100:100:100::100
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 3/5/12 ms
d_CE1#
d_CE1#traceroute 1125:200:200:200::200 source 1125:100:100:100::100
Type escape sequence to abort.
Tracing the route to 1125:200:200:200::200

  1 1125:1010:20::1 [AS 1] 6 msec 2 msec 2 msec
  2 1125:1:2::2 [MPLS: Label 24008 Exp 0] 8 msec 5 msec 4 msec
  3 1125:1010:30::3 [MPLS: Label 24004 Exp 0] 10 msec 8 msec 10 msec
  4 1125:3:4::4 [MPLS: Label 24002 Exp 0] 5 msec 3 msec 4 msec
  5 1125:1010:80::2 [AS 2] 4 msec 3 msec 4 msec
d_CE1#
d_N1(PEルータ)からCE2’s Loopback0(1125:200:200:200::200/128)に到達するには、
RD 1:1 で route-target 400:2 を使う
NEXT_HOP は 1125:2:2:2::2 (Label 24008)

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N2(ASBRルータ)ではこのようになりました。

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N3(ASBRルータ)ではこのようになりました。

パケットも見てみましょう。showコマンドと一致していることが分かります。

d_N4(PEルータ)ではこのようになりました。

8. 参考URL
① Configuration and Verification of Layer 3 INTER-AS MPLS VPN Option B using IOS and IOS-XR
www.cisco.com
② Cisco IOS-XR BGP with MPLS Designs
www.cisco.com
③ Introduction Inter-AS L3VPN
https://nsrc.org/workshops/2015/apricot2015/raw-attachment/wiki/Track3MPLS/9-Apriot_2015_Inter-AS.2.pdf
④ [Multi-AS Segment Routing 検証連載 #2] SR-MPLS L3VPN in Multi-AS
engineers.ntt.com
⑤ Inter-AS Option B
gemunopedy.hatenadiary.com
⑥ Inter-AS Option B
chimay-wh.hatenablog.com
次回は、Inter-AS Option C(IOS-XE & IOS-XR)について記事を書きます。
最後までお読みいただきありがとうございました!
